ZK/SEC Research notes from zkSecurity
All posts
announcement · zk

zkBitcoin: Use Zero-Knowledge Applications (zkapps) on Bitcoin

zkbitcoin

In collaboration with Σ0, we released a new primitive called zkBitcoin, which allows for the creation of zero-knowledge applications (zkapps) on Bitcoin via a minimal layer 2 protocol that uses Bitcoin as data availability layer and a committee of participants to perform threshold signatures.

This is a significant milestone for the Bitcoin ecosystem as it augments the capability of the Bitcoin scripting language allowing for larger and more complex application. In addition, it unlocks privacy-preserving applications for Bitcoin.

We're currently running on testnet, and you can try it out by downloading the zkBitcoin CLI.

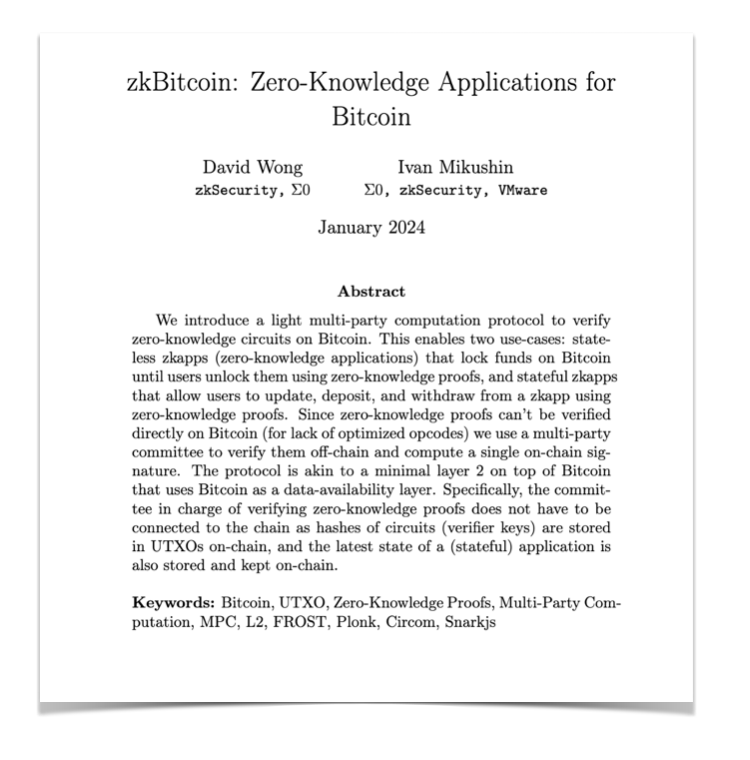
You can read the whitepaper here, which describes the two types of zkapps that can be created, stateless and stateful, while providing more details about the protocol overall:
zkbitcoin

If you like videos, you can watch an overview of the project:

a walkthrough of the whitepaper:

and a walkthrough of the codebase:

We're excited to see what people will build on top of zkBitcoin. If you're interested in running a node for the network, or interested in using the protocol for your own application or L2, shoot us a message!

Keep reading
Recommended

Archetype x zkSecurity - Proof is in the Pudding: ZK on Bitcoin

In Session 09 of "Proof is in the Pudding," we explore the intersection of zero-knowledge proofs and Bitcoin. We break down Bitcoin's UTXO model and Script limitations, then dive deep into approaches for verifying ZK proofs on Bitcoin, from MPC-based techniques to BitVM's optimistic verification with fraud proofs. We cover timelocks, the statelessness problem and Lamport signatures for state, Taproot, simulated covenants, BitVM 3 with hashlocks and garbled circuits, cut-and-choose security, and witness encryption (BABE).

ZK/SEC · April 02, 2026

Reproducing and Exploiting ZK Circuit Vulnerabilities

Check out our latest blog post where we dive into the world of Zero-Knowledge Proof (ZKP) vulnerabilities, sharing our insights from replicating known ZK circuit weaknesses. We’ve launched a GitHub repo with detailed scripts to help you understand, reproduce, and learn from these vulnerabilities. Discover how this hands-on approach aids in grasping attack vectors, testing fixes, and enriching educational resources. Whether you're a researcher or a developer, this post is packed with info to enhance your knowledge and skills in ZKP security. Plus, find out how you can contribute to expanding this invaluable resource!

Stefanos Chaliasos, Chenyang Yu · August 09, 2024

zkSecurity took part in judging the latest zkHack Montreal

We recently had the thrill of judging the latest zkHack competition in Montreal, where developers, researchers, and enthusiasts dove into the world of zero-knowledge proofs and privacy tech. The projects were incredibly innovative, featuring creative applications like ZK breathalyzers and ZK & GPS solutions. Check out the exciting results and insights from this year's event. You won't want to miss what these brilliant minds are bringing to the table!

ZK/SEC · September 02, 2024
More to explore

Public report of Sui's zkLogin audit

We just finished an audit of the Sui Foundation's zkLogin application and we're sharing what we found: the code is well-documented, tested, and specified. The zkLogin is set to make user authentication on the blockchain secure but simple, replacing cryptographic keys with familiar SSO methods like Google or Facebook while preserving user privacy. We also dive into the technical details behind JWT verification, non-native arithmetic for RSA, and vector programming. Plus, learn about the trusted setup process for zkLogin, ensuring maximum security through a decentralized multi-party ceremony. If you're curious about the intricate mechanics behind zkLogin, this is a must-read.

ZK/SEC · November 07, 2023

Partnership with StarkWare

We're teaming up with StarkWare to enhance Ethereum's scalability using an exciting tool called the EVM adapter. This innovative open-source project takes proofs from the Stone Prover and makes them verifiable on Ethereum, showcasing the power of Cairo bootloader programs for Layer 2 scaling. By diving into our collaboration, you'll get a glimpse of StarkNet's ability to streamline transactions efficiently and how our joint efforts are driving this tech forward. Plus, our Stark Book offers a deeper technical dive for the curious minds!

ZK/SEC · April 05, 2024

noname 2.0: Unlocking Numeric Generics, Folding Schemes, and a Playground

We're excited to introduce the preview of noname 2.0, packed with features that make developing advanced ZK circuits easier than ever. This update includes flexible generic-sized arrays, seamless integration with folding schemes for IVC, and an interactive online playground to test and share code. We've also optimized R1CS constraint generation to boost performance. Plus, there are numerous community-driven enhancements and bug fixes that make the language more robust and user-friendly. Dive in to explore the specifics of our journey, learn from the contributions of our vibrant open-source community, and see how noname is evolving into a more versatile tool for developers.

ZK/SEC · August 08, 2024